📊 Full opportunity report: Security Checklist For Remote Work Devices With Mixed Hardware on IdeaNavigator AI — validation score, market gap, and execution plan.
Get ready for Prime Big Deal Days — try Prime free
Exclusive member deals on October 6–7, plus fast free delivery. Cancel anytime.
Start your free trialAs an affiliate, we earn on qualifying purchases.
TL;DR
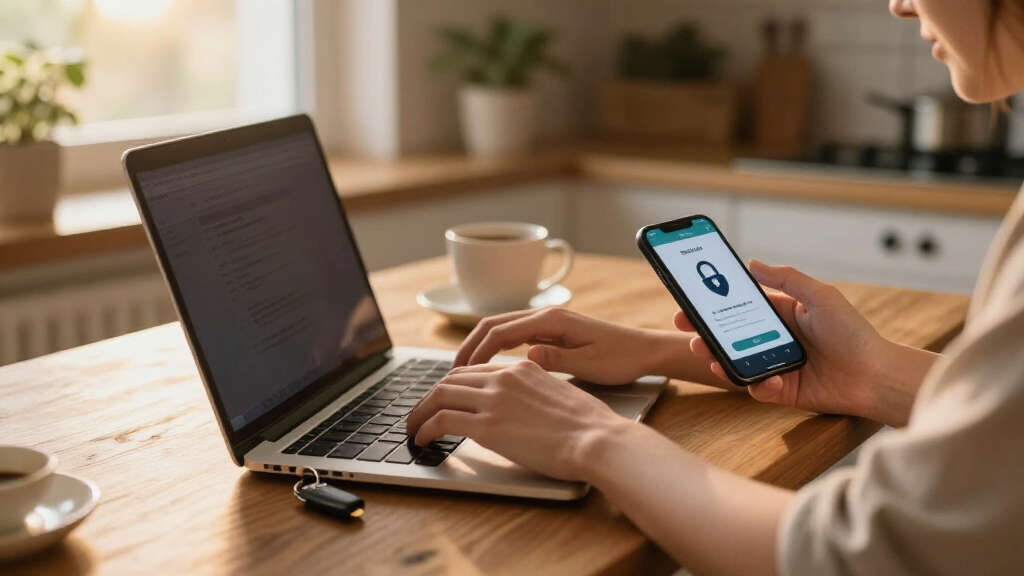
A new lightweight security tool for remote teams with mixed hardware aims to verify device compliance. It addresses gaps in encryption, updates, and security posture, helping SMBs meet compliance standards.
A new lightweight device security checker designed for remote teams with mixed hardware is entering pilot testing, targeting SMBs needing to meet compliance standards such as SOC 2. The tool allows employees to voluntarily install an agent that assesses device encryption, OS updates, screen lock status, and password manager presence, reporting results to security teams without remote control capabilities. This development responds to a growing compliance verification gap caused by employee-owned devices and the limitations of traditional MDM solutions.
The security checker is aimed at operations and security leads at remote companies with diverse hardware, including personal MacBooks, aging Windows laptops, and unmanaged smartphones. Currently, many organizations lack visibility into whether these devices meet basic security standards such as disk encryption, timely OS updates, and screen locks, which are critical for compliance with standards like SOC 2. The new tool offers a simple, voluntary agent that performs these checks and reports pass/fail status to a dashboard, enabling teams to identify vulnerabilities quickly and provide self-remediation instructions.
According to an anonymous researcher involved in the project, the approach is designed to fill a verification gap that traditional MDM solutions cannot address due to their invasiveness or complexity on employee-owned devices. The tool is priced per device monthly, with additional features such as compliance report exports available on paid tiers. Initial deployment at ten remote startups will measure device enrollment rates and gauge whether auditors accept the reports as sufficient evidence of security posture, aiming to validate its effectiveness for SMBs facing increasing regulatory scrutiny.
Implications for SMBs and Compliance Verification
This development is significant because it offers a scalable, non-invasive way for SMBs to verify security compliance across a diverse range of employee-owned devices. As standards like SOC 2 become more widespread and audits more rigorous, organizations need efficient methods to demonstrate device security without overhauling their existing hardware or infringing on employee privacy. The tool’s ability to provide automated, self-service checks could streamline compliance workflows and reduce audit preparation costs, making it a valuable addition to endpoint security strategies for remote teams.
device encryption verification tool
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Growing Challenges in Securing Remote, Mixed Hardware Environments
The rise of remote work has expanded the diversity of hardware used by employees, complicating security management for organizations. Many SMBs rely on personal devices for work, but traditional endpoint security solutions like mobile device management (MDM) often prove too invasive or cumbersome for employee-owned hardware. This has created a verification gap, especially as security standards such as SOC 2, which require demonstration of controls like disk encryption and timely updates, become more enforceable. Existing solutions often focus on corporate-owned devices, leaving unmanaged personal devices as weak links in security postures.
Recent industry discussions highlight the need for lightweight, voluntary tools that can assess device security without infringing on privacy or requiring extensive infrastructure. The new device checker aims to address this gap by providing a simple, self-installable agent that reports compliance status, aligning with the trend toward more flexible, privacy-conscious security solutions for remote workforces.
remote device security compliance checker
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Uncertainties Around Adoption and Regulatory Acceptance
It is not yet clear how quickly organizations will adopt this new security checker or whether auditors will accept its reports as sufficient evidence of compliance. The initial pilot at ten startups will provide some insights, but broader industry validation remains pending. Additionally, questions remain about how the tool will handle diverse device configurations and whether it can reliably detect all relevant security issues across different OS versions and hardware types. The long-term impact on compliance workflows and privacy considerations is also still under discussion.
As an affiliate, we earn on qualifying purchases.
Next Steps for Deployment and Industry Validation
The initial deployment at ten remote startups will test device enrollment rates, user acceptance, and auditor feedback. Based on these results, the developers plan to refine the tool and expand its availability to more SMBs. Further, they aim to establish partnerships with compliance auditors to ensure the reports meet regulatory standards. Additional features such as automated remediation guidance and integration with existing security platforms are also under consideration to enhance usability and effectiveness. The upcoming months will reveal whether this approach can become a standard part of remote endpoint security management.
As an affiliate, we earn on qualifying purchases.
Key Questions
How does the device security checker work?
The tool involves employees voluntarily installing a lightweight agent that performs checks on encryption, OS updates, screen lock status, and password manager presence. It then reports pass/fail results to a dashboard for security teams to review.
Will this tool replace traditional MDM solutions?
No, it is designed as a lightweight supplement for verifying device security, especially on personal and unmanaged devices where MDM is too invasive or impractical.
Is this tool suitable for all types of devices?
The initial focus is on common SMB devices, including Macs, Windows laptops, and smartphones. Compatibility and effectiveness across all hardware types will depend on future development and testing results.
Will this meet compliance requirements like SOC 2?
Initial testing aims to confirm whether security posture reports generated by the tool are accepted by auditors as sufficient evidence of compliance, but full validation is still in progress.
What are the privacy implications for employees?
The tool is designed to perform only security checks without invasive access or remote control, aiming to respect employee privacy while providing necessary compliance data.
Source: IdeaNavigator AI
Fall Picks
fall essentials
As an affiliate, we earn on qualifying purchases.